Blog
Insights on digital sovereignty, automation, and reliable infrastructure.
Subscribe via RSSCase Studies
Need something closer to delivery than a standard blog post?
The Proof section turns anonymized delivery experience into compact implementation stories: practical structure, concrete technology choices, and business-relevant outcomes without portfolio theatre.
Rancher 2.15 Monitoring Migration: The Missing Practitioner Runbook
A battle-tested migration guide from legacy rancher-monitoring to upstream kube-prometheus-stack and rancher-monitoring-dashboards, including CRDs, PVCs, custom dashboards, and Alertmanager.
CADA and NIS2: review cloud vendors and evidence
Which requirements apply already, and which are proposed? How SMEs can review cloud vendors and maintain contracts, access records and evidence.
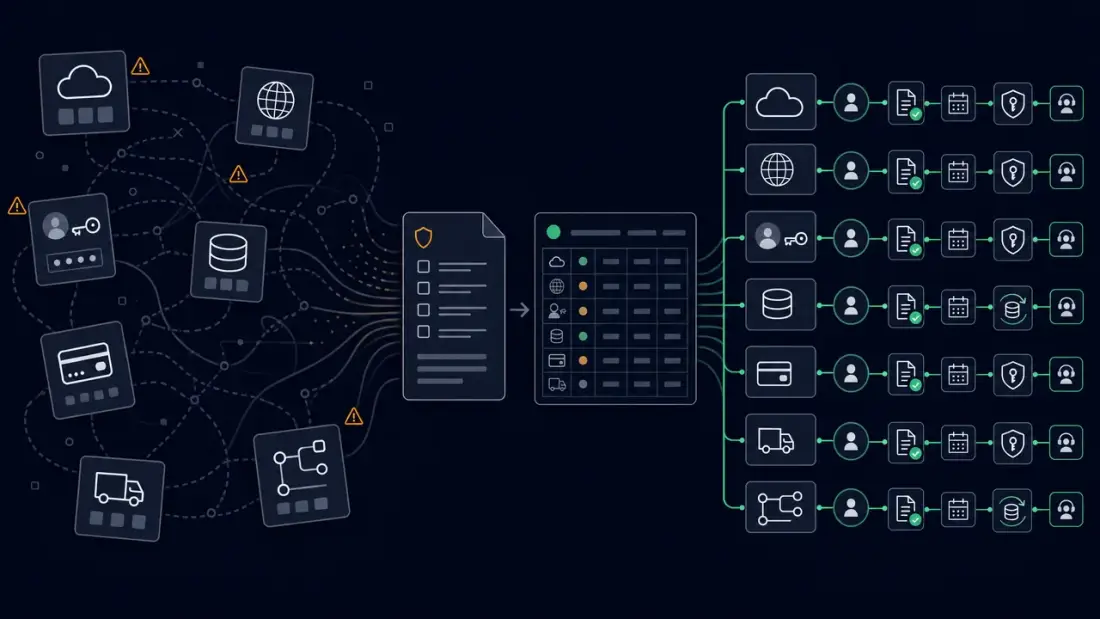
NIS2 and the Supply Chain: Why Your Vendors' Security is Now Your Problem
NIS2 turns supplier security into an operational evidence problem for many SMEs: who processes data, who has admin access, who reports incidents, and which proof exists? This guide shows how to build a lightweight vendor-risk workflow.
NIS2 Readiness: Why Cybersecurity Now Needs an Operating Model
For many SMEs, NIS2 will first appear as customer questionnaires, supplier checks, or incident pressure rather than legal theory. This guide explains the operating model that makes readiness practical: asset inventory, ownership, runbooks, supplier control, and evidence.
Beyond the Dashboard: Why Manual Monitoring Is a Business Risk
Dashboards are not operations. Learn why manual monitoring delays incident response and how SMEs and startups can move toward practical observability, runbooks, and owned digital operations.
Backup Anxiety: Why Having a Backup Isn't the Same as Having a Recovery Plan
Many businesses think they are safe because they have "backups." But a backup you haven't tested is just a hope. Learn how to turn backup anxiety into recovery confidence.