Security by Architecture: Why Cybersecurity Cannot Be an Add-on
Security failures often start with unclear architecture, not missing tools. Learn how SMEs and startups can design a Digital Headquarters with cleaner access, backups, automation, and recovery paths.
Contents
Security failures often start with unclear architecture, not missing tools. Learn how SMEs and startups can design a Digital Headquarters with cleaner access, backups, automation, and recovery paths.
Share this article
The morning security becomes an architecture problem
It starts unremarkably. A suspicious login in the company mailbox. A contact form that stopped sending messages. An invoice that never went out because an automation tool lost its API credentials. The IT support team is called — and nobody can immediately say which systems, accounts, and automations are involved.
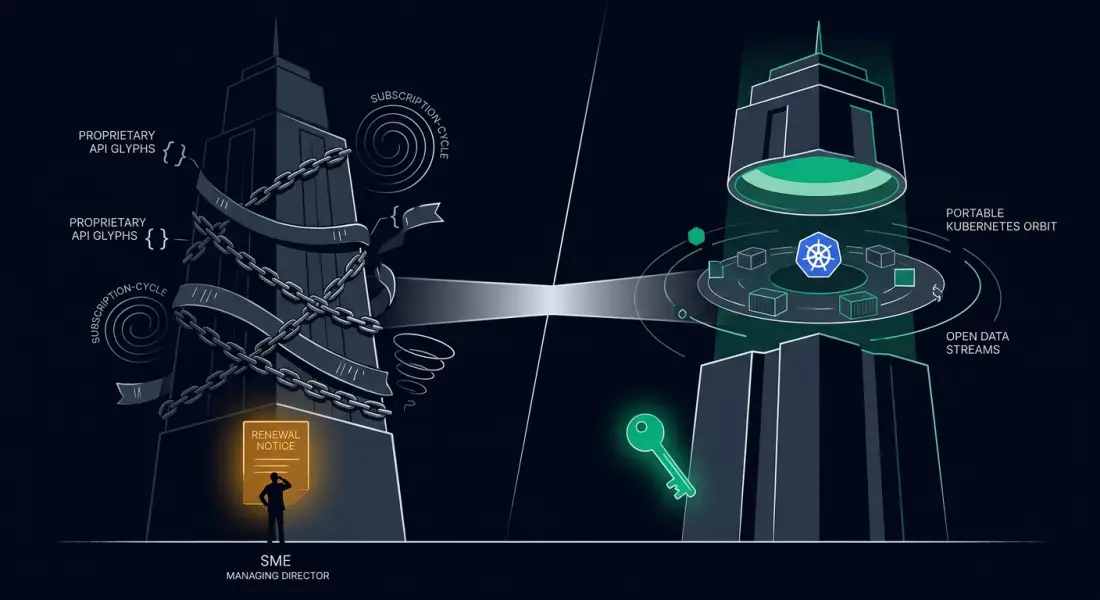
For many small businesses and startups, this is not an exception. It is a condition that crept in gradually. The infrastructure grew over months and years: a web host, a cloud storage solution, an accounting tool, a few automations between email, CRM, and calendar, maybe a n8n workflow set up two years ago by someone who has since left. Each tool individually sensible. Together, they form a system nobody fully understands.
That is where the problem lives. Security does not usually fail because a tool was missing. It fails when nobody can fully see how the digital machine runs — when nobody can say who has access, which automation is running, which backup is current, and who keeps the overview when things go wrong. A well-designed security architecture is more than protection: it is a business enabler that speeds up decisions, simplifies audits, and builds trust with customers and partners.
Why add-on security feels productive but leaves the core fragile
It is understandable that a new scanner, a password tool, or a compliance checklist can feel like progress. The business can point at something and say: work is happening. But if the underlying architecture remains unclear, the risk does not disappear. It just becomes harder to see.
The problem is not that security tools are inherently useless. The problem is that tools cannot replace what architecture is missing: clear ownership, documented automations, known backup paths, and controlled handovers.
Tools cannot fix unknown ownership
A security scanner can report an open port. It cannot say whether this automation is still active, who created it, and whether it is still being monitored after an employee left. A password policy can mandate that passwords be complex. It cannot prevent ten people from sharing the same admin account because separation was never set up.
Compliance checklists do not replace operating discipline
A compliance audit can confirm that certain controls are documented. It cannot replace what actually happens in practice: who changed something in the system this week? Which tool moved customer data? Where are the logs? Which backup was last tested? Who is the escalation point?
The real cost of add-on security
Time lost finding the system map
ENISA notes that SMEs are particularly vulnerable because their digital infrastructure often grew without systematic planning. When a security incident occurs, the search for the cause becomes archaeology: Who had access? Which automation moved data? Which backup is current? Why did nobody notice the open interface?
In a Ponemon and IBM study, the average time to identify and contain a data breach was 277 days. For small companies without a dedicated security team, that timeline is even more problematic — not because the technology is worse, but because the personnel and process resources to move quickly are missing.
Money lost to rework, downtime, and forced vendor dependence
Unclear architecture turns routine security work into expensive external dependency. When an incident hits, emergency support is needed immediately. Migration under time pressure, manual cleanup, premium support contracts, rushed audits, rebuilds under duress.
Veeam's 2024 Data Protection Trends Report found that 93 percent of organizations hit by ransomware said their backup recovery was partially or completely unsuccessful. 87 percent of all surveyed organizations said their backups fail to restore when needed.
Rubrik Zero Labs reported for 2023 that 97 percent of ransomware attacks deliberately targeted backup data. Backup systems that were never tested offer no real protection at that moment. They offer a false sense of control.
The security architecture map
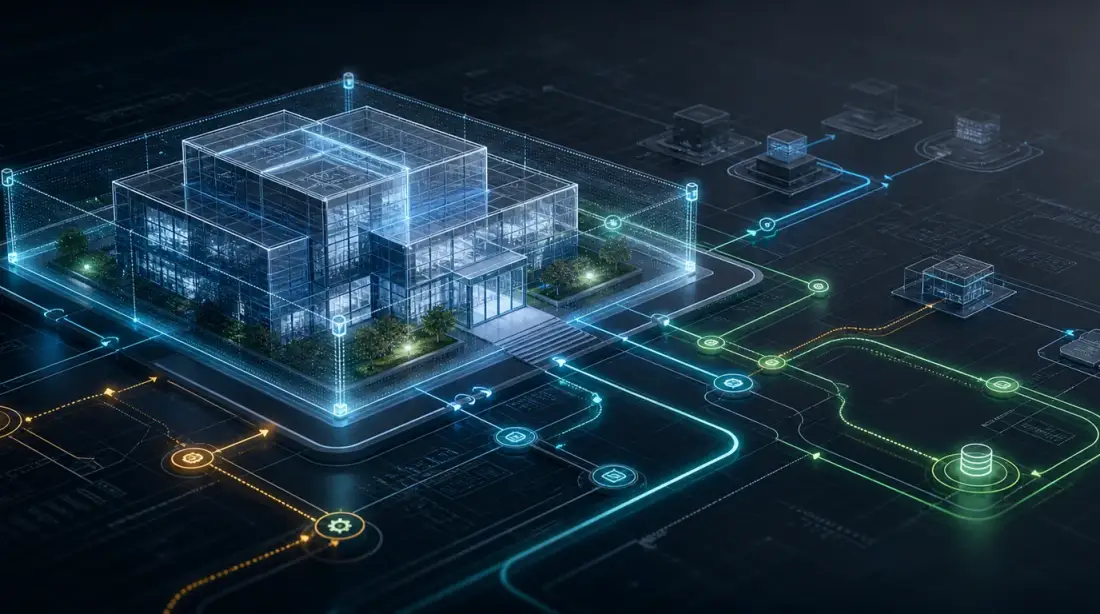
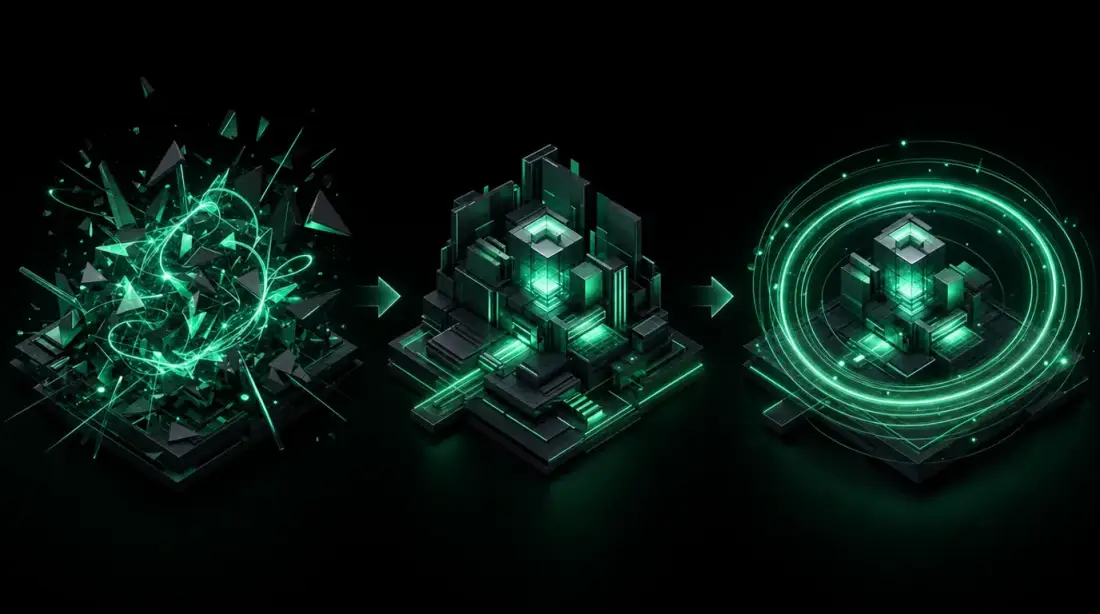
A reliable Digital Headquarters does not need an enterprise-grade tool landscape. It needs an architecture that shows how business processes, data flows, identity, automation, observability, and recovery connect.
The image below shows how the layers of a security architecture work together for small and medium businesses — from business processes and data flows through identity and access control, automation and deployment, to observability and recovery.
Identity, access, and secrets
The first control point is straightforward: who has access — and for what purpose? The principle of least privilege means employees can only see and change the systems and data necessary for their work. Role separation ensures admin accounts are not used for routine tasks. MFA protects accounts against compromised passwords.
Offboarding is a critical, often underestimated moment. When an employee leaves, all access must be deactivated, API keys revoked, and shared accounts cleaned up. In many SMEs, inactive accounts persist because no defined process exists — a latent risk that regular access reviews reduce.
API tokens and secrets deserve special attention. Automations and integrations often use long-lived access tokens. These are rarely rotated, often undocumented, and can offer a wide attack surface if they fall into the wrong hands.
Deployment, automation, and change control
Changes to infrastructure should be traceable. Git-managed infrastructure means configuration changes are treated as code and versioned. CI/CD pipelines with review gates ensure no unauthorized or untested change reaches a production environment.
Automation workflows — for example in n8n or similar tools — also need ownership and documentation. Who created a workflow? What happens when a trigger credential expires? Is there a rollback path if an automation behaves unexpectedly?
For environment separation: a development and a production system should have separate access and ideally separate infrastructure. This prevents changes in testing from accidentally affecting production data.
Observability, backups, and recovery
Logs and alerts are worthless if nobody reviews them regularly. A minimal observability stack for small companies includes: centralized logs from the most critical systems, an alerting system for critical events (e.g., failed logins, unexpected configuration changes), and a clear escalation plan.
Backup tests are the most commonly skipped routine in small companies. The good news: a monthly restore test of one file or database is quick to do. It shows whether the backup is complete, current, and recoverable. Veeam's data shows that organizations that test regularly recover from outages far faster when an incident occurs.
For recovery, a realistic Recovery Objective is needed: how much data loss is acceptable? Within what time must the system be available again? Who makes the call on whether to restore from a specific backup?
Proof: From tool patchwork to governed operations
Let us analyze a concrete scenario — illustrative, but familiar from practice. A mid-sized mechanical engineering firm with 35 employees. Every year, approximately 180 active projects run through the office. Managing director Klaus has built a digital infrastructure over the years: a WordPress website with inquiry forms, Microsoft 365 for email and documents, a CRM for client management, an accounting tool, and several n8n automations between email, CRM, and project management. Sarah Hoffmann, the office manager, coordinates customer contact, scheduling, and internal workflows.
Before: A business that depends on memory
In the current state, the digital infrastructure operates blindly. Shared admin accounts for the website, CRM, and cloud storage are tied to two key people — Klaus and an external IT service provider whose exact access rights were never documented. Several API keys for n8n workflows were created over a year ago; nobody knows for sure whether they are all still active.
When Sarah offboarded an accounting employee in spring 2025, it took weeks to notice that the employee's CRM access via a shared account was still working. An automated invoice export hung silently for three days because an expired API token triggered no alert. Monthly backups showed green — yet nobody had run a restore test in the past 14 months.
The problem is not one dramatic incident. The problem is accumulated ambiguity: shared admin accounts, unknown API keys, undocumented workflow owners, weak backup verification, and no single deployment or recovery path. When Klaus is unavailable for three days, decisions stall because nobody has the full system overview.
After: A digital machine with evidence
The improvement is step-by-step and realistic:
-
Asset inventory: All systems, accounts, automations, and data flows are catalogued. The result is a current system map with named owners. Klaus keeps strategic responsibility; Sarah is named for operational access management and routine checks.
-
Role model: Clear access groups replace shared accounts. MFA is enabled for all admin accounts. Offboarding processes are defined: when an employee leaves, Sarah checks all related accounts within 24 hours and documents the deactivation.
-
Secrets review: All active API keys and service accounts are documented, checked for necessity, and renewed where needed. Tokens with unknown purpose are deactivated.
-
Git-based deployment: Infrastructure and configuration changes are versioned, tested, and delivered through a CI/CD pipeline. Klaus sees before approving every deployment what is changing and why.
-
Automation inventory: All n8n workflows are captured, assigned owners, and checked for error rates and credential expiry. Sarah runs a monthly brief on active workflows and exceptions.
-
Decision points and review gates: Inquiries over a project volume of EUR 30,000 are automatically marked as high-priority in the CRM and routed to an approval gate. Klaus personally reviews and approves these inquiries before a proposal is sent. Every approval is logged with timestamp and reviewer.
-
Monitoring: Logs are centralized, alerts for critical events are configured. Sarah receives a daily summary of failed logins and unexpected configuration changes.
-
Backup restore test: Monthly restoration tests are established as a routine and documented. Sarah runs a test restore every first Tuesday of the month and confirms recoverability in writing.
-
Lightweight incident playbook: A short document describes who does what when an incident occurs — including escalation, communication, and recovery steps. Klaus decides on external communication; Sarah coordinates internal measures.
-
Audit trail: All access changes, approvals, and incident steps are recorded in a tamper-proof log. This not only makes incidents traceable, but also speeds up future audits and insurance conversations.
The outcome is not "perfect security." The outcome is a system that can be understood, tested, restored, and improved. Faster decisions, fewer unknowns, cleaner handovers, clearer ownership — and an operation that keeps running even when individual people are unavailable.
More on this in our proof format for infrastructure modernization:
How Planfold frames secure digital operations
The question small companies should ask is not: "Are we missing a security tool?" It is: "Do we understand how our digital machine works?"
Planfold works with a Plan -> Unfold -> Resonate method that operationalizes exactly this question:
Plan — Map the real risk surface
Before another tool is bought, the actual assets, data flows, accounts, automations, and dependencies are captured. What is critical? What happens if it fails? Who has access? What are the recovery requirements?
Unfold — Build controls into the system
Implementation means creating an owned architecture: access model, automation documentation, CI/CD discipline, tested backups, monitoring, and incident routine. Not as a project with a finish date, but as an ongoing operation.
Resonate — Keep security operational
Continuous monitoring, regular updates, reviews, and visible operational confidence. This includes treating security routines not as a one-time action but as a recurring process. That is the difference between a system that was temporarily hardened and a system that is understood and maintained.
Compliance as a trust signal, not bureaucracy
A clear security architecture is not purely a cost factor. It speeds up audit conversations because evidence is tangible. It strengthens trust with customers and partners because the business can explain who has access and how data is protected. And it reduces friction in supply chains: anyone working with larger clients or regulated industries quickly finds that security evidence is no longer a nice-to-have, but a prerequisite for collaboration. With the NIS2 Directive, expectations on suppliers are rising especially in sensitive sectors. Those who can document their architecture gain a competitive advantage — not because they do everything perfectly, but because they can provide evidence.
A practical starting point for SMEs and startups
Start with one critical workflow
The question "Where do we start?" is best answered concretely: start where an outage would cost the most — or where a security problem is most likely.
A practical start: choose a customer-facing or revenue-critical workflow. For that workflow, inventory the accounts, systems, data, automations, logs, and recovery paths. Document the current state — not perfectly, but as completely as possible. Name a responsible owner and a deputy for absences.
The result is a first map. From there, systematic improvement becomes possible: clean up access, renew secrets, document workflows, test backups, enable monitoring.
Make the safe path easier than the improvised path
Security becomes a habit when the approved path requires less effort than the improvised one. Automations that only work with documented credentials. Workflows that only run on documented systems. A way of working that defines the secure path as the easy path.
The real outcome: A business you can understand under pressure
Security by architecture does not mean building the perfect security system. It means having a system you understand, can operate, can restore, and can improve.
You are not buying another security solution. You are building a Digital Headquarters that will not become a mystery in a crisis — and that will help you understand how your machine really works even when no crisis occurs.