Sovereignty through Architecture: Why Cloud-Exit is a Leap Forward
Moving away from hyperscalers isn't a step backward, it's a strategic decision for cost control, privacy transparency, and vendor independence. Here's what decision-makers need to know.
Contents
Moving away from hyperscalers isn't a step backward, it's a strategic decision for cost control, privacy transparency, and vendor independence. Here's what decision-makers need to know.
Share this article
The Hidden Cost of Convenience
Every month, your finance team approves another cloud invoice. The numbers fluctuate unpredictably, sometimes 15% higher, sometimes 30%. You've accepted this as the cost of doing business in the digital age. Honestly, have you ever stopped to ask what you're actually paying for?
For many organizations, the promise of cloud computing has become a dependency trap. What started as flexibility evolved into vendor lock-in. What was sold as scalability became unpredictable spending. And what was marketed as innovation quietly shifted control of your data to jurisdictions you never chose.
Digital sovereignty isn't a buzzword. It's the difference between owning your infrastructure and renting someone else's rules. The answer to "Who controls your corporate data?" is often uncomfortable. Here's why a strategic cloud-exit isn't a step backward.
Financial Independence: From Variable Costs to Predictability
The OPEX Problem of Public Cloud
The billing model of major cloud providers follows a simple logic: the more you use, the more you pay. That sounds fair, until you look at the reality of business practice.
Typical scenarios that lead to cost explosions:
- Traffic spikes from marketing campaigns double the monthly bill
- Forgotten test environments continue running unnoticed
- Database scaling happens automatically, without prior approval
- Outbound data transfer is billed per gigabyte
A realistic planning scenario shows the pattern: when a misconfigured storage resource goes unnoticed for months, the bill can climb sharply without corresponding business growth. The real damage is not only the amount, but the loss of cost control.
CAPEX as a Strategic Asset
The alternative is as old as IT itself, but more relevant than ever: investments in your own infrastructure create assets.
| Aspect | Public Cloud (OPEX) | Sovereign Infrastructure (CAPEX) |
|---|---|---|
| Cost Planning | Variable, hard to predict | Fixed, budgetable |
| Tax Benefits | Operating leasing | Depreciation, investment deduction |
| Negotiating Power | Dependent on provider | Independent, own resources |
| Exit Costs | Data export, migration | None, you're the owner |
Illustrative model: A company with 50 employees and an average IT load might pay approximately €2,400 monthly for cloud services. That's €28,800 annually, money that's gone at the end of the year.
Comparable performance on owned or dedicated infrastructure might require an initial investment of approximately €35,000. Whether and when that investment amortizes depends on workload profile, operating costs, maintenance, staffing, and contract terms. Those factors need to be modeled before a cloud-exit decision.
The Predictability Effect
For CFOs and managing directors, the predictability of IT costs is a strategic advantage. Budget conversations become easier, investment decisions more transparent, and the risk of unpleasant surprises disappears.
Here's why this matters: a robust forecast can show which costs become fixed, which remain variable, and where dedicated infrastructure starts to make economic sense. For CFOs and managing directors, that predictability can matter more than the monthly invoice alone.
Data Privacy and Compliance: Where Your Data Really Lives
The GDPR Reality
The General Data Protection Regulation has been in force since 2018, but the question of data localization remains unclear for many companies. When data is processed in a public cloud, companies need to understand exactly where data is stored, processed, backed up, and administered.
Why the Cloud Act appears in risk reviews: The US Cloud Act of 2018 can be part of the legal risk assessment for US providers, even when data is physically stored in Europe. Whether it creates a concrete risk depends on the provider, contract model, data type, encryption, technical controls, and case-specific legal assessment.
The Consequences for European Companies
Lawyers and data protection officers increasingly review these constellations in more detail. A company processing customer data through a non-European cloud provider should clarify:
- Which parties could have technical or organizational access to data
- Which GDPR records, processor agreements, and transfer mechanisms are required
- Which responsibilities apply in case of data incidents, support access, or authority requests
The Solution: Data in Austria and Germany
Sovereign infrastructure or hosting with European providers can make the assessment clearer. Data locations, administrator access, and technical safeguards can be documented and controlled more deliberately. This is not a substitute for legal review, but it gives privacy and compliance teams a clearer basis for decisions.
For compliance officers, this means:
- Clear documentation of data processing location
- Better assessment of possible third-country transfer risks
- Easier-to-review GDPR documentation
- Clearer processes for authority requests and internal evidence
Built-in compliance: When sovereignty is planned from the start, evidence does not have to be assembled right before an audit. Data flows, access rights, backup locations, logging, and responsibilities become part of the architecture documentation instead of a last-minute research task.
| Traditional Cloud | Sovereign Infrastructure |
|---|---|
| Compliance as add-on service | Compliance as default state |
| Data residency requires configuration | Data residency by design |
| Audit trails need enabling | Audit trails always active |
| Privacy as policy | Privacy as architecture |
Vendor Independence: Freedom Through Architecture
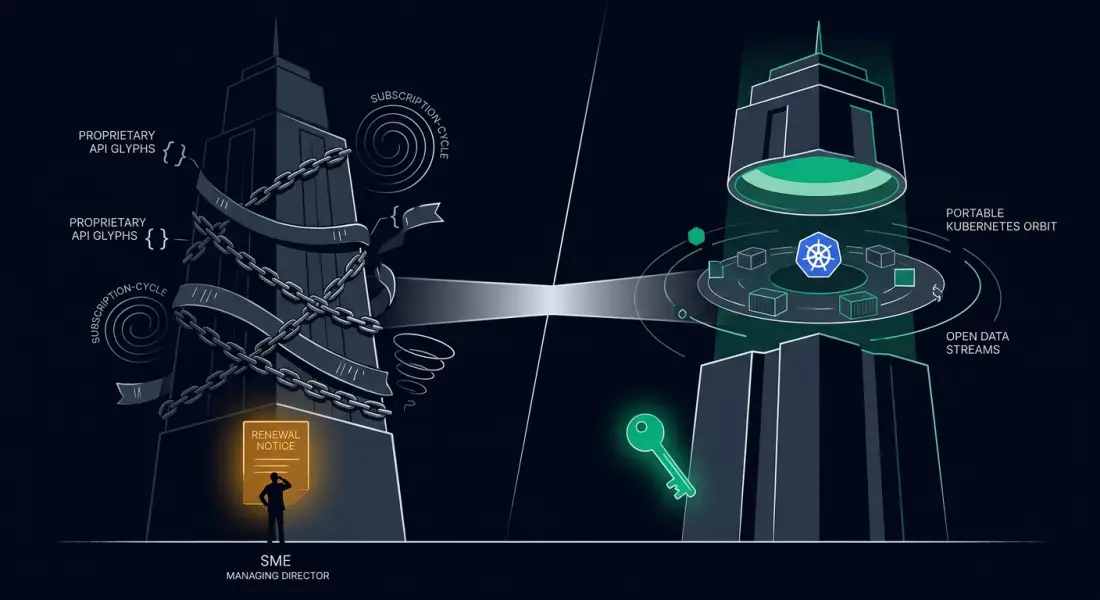
Vendor Lock-in: The Invisible Chain
Dependencies develop gradually. A company starts with a simple database in the cloud, adds storage services, integrates authentication services, and suddenly the entire IT architecture is aligned with one provider.
The costs of switching grow exponentially:
- Data migrations are complex and risky
- APIs and integrations must be redeveloped
- Team training is necessary
- Business interruption during migration costs revenue
The result: companies stay with a provider even when performance no longer convinces or prices rise.
The Architecture of Autonomy
Strategic cloud-exit is more than a migration. It's the opportunity to redesign IT architecture with independence as a core principle.
Key principles of a sovereign architecture:
- Open standards instead of proprietary services: What's based on standard technologies is portable
- Documented processes: Every step is traceable and reproducible
- Modular structures: Components can be exchanged without endangering the overall system
- Automation: Repeatable tasks run without manual intervention
Technical sovereignty through open source: We achieve true independence through Kubernetes (K3s), Rancher orchestration, and Infrastructure as Code (IaC). These aren't just tools, they're industry standards that ensure your infrastructure remains portable, vendor-neutral, and future-proof. No proprietary lock-in, no "back to hardware" image, just modern cloud-native architecture on your terms.
Concrete Business Value
| Independence | Business Benefit |
|---|---|
| Negotiating Power | Better terms with hardware and service providers |
| Agility | Faster response to market changes |
| Risk Minimization | No single points of failure through provider dependency |
| Future-Proofing | Investments in competencies, not dependencies |
A typical negotiation scenario: a company discovers that a critical database service has become significantly more expensive, but cannot move quickly because its data model, integrations, and operations are tightly bound to the provider. A documented exit strategy does not automatically lower prices, but it gives the company options again.
Cloud-Exit as Strategic Decision
Digital sovereignty isn't a technical luxury. It's a question of entrepreneurial self-determination. Those who retain control over their data, cost structure, and IT architecture remain capable of acting, today and in the future.
The three pillars of sovereignty:
- Financial predictability through investments instead of variable expenses
- Compliance transparency through traceable data localization and clear access concepts
- Freedom of action through independent architecture
The step back from public cloud isn't an admission of technical backwardness. It's a conscious decision for architecture that serves the company, not the other way around.
Examine your current IT landscape for dependencies. Where are incalculable costs arising? Where are your data flows going? Who has control?
The answers could be the beginning of your sovereignty strategy.
Ready to assess your path to sovereign infrastructure? Get in touch for a confidential consultation.